
Your infrastructure, run by private AI.
Servers, cloud accounts and Kubernetes in one console, with security built in. Ask Garry, get answers from read-only checks, and approve every change. Nothing changes until a person says so.
One box. Agents connect out. People approve.
Install
One command turns an NVIDIA DGX Spark into the appliance: console, models, monitoring.
Connect
One-line agents on Linux and Windows; cloud, Kubernetes, SIEM and firewall connectors.
Operate
Ask Garry, run checks and schedules, watch logs and metrics; alerts become cases.
Approve
Every change shows its exact command, waits for a person, runs, is verified and audited.
The estate, in one conversation.
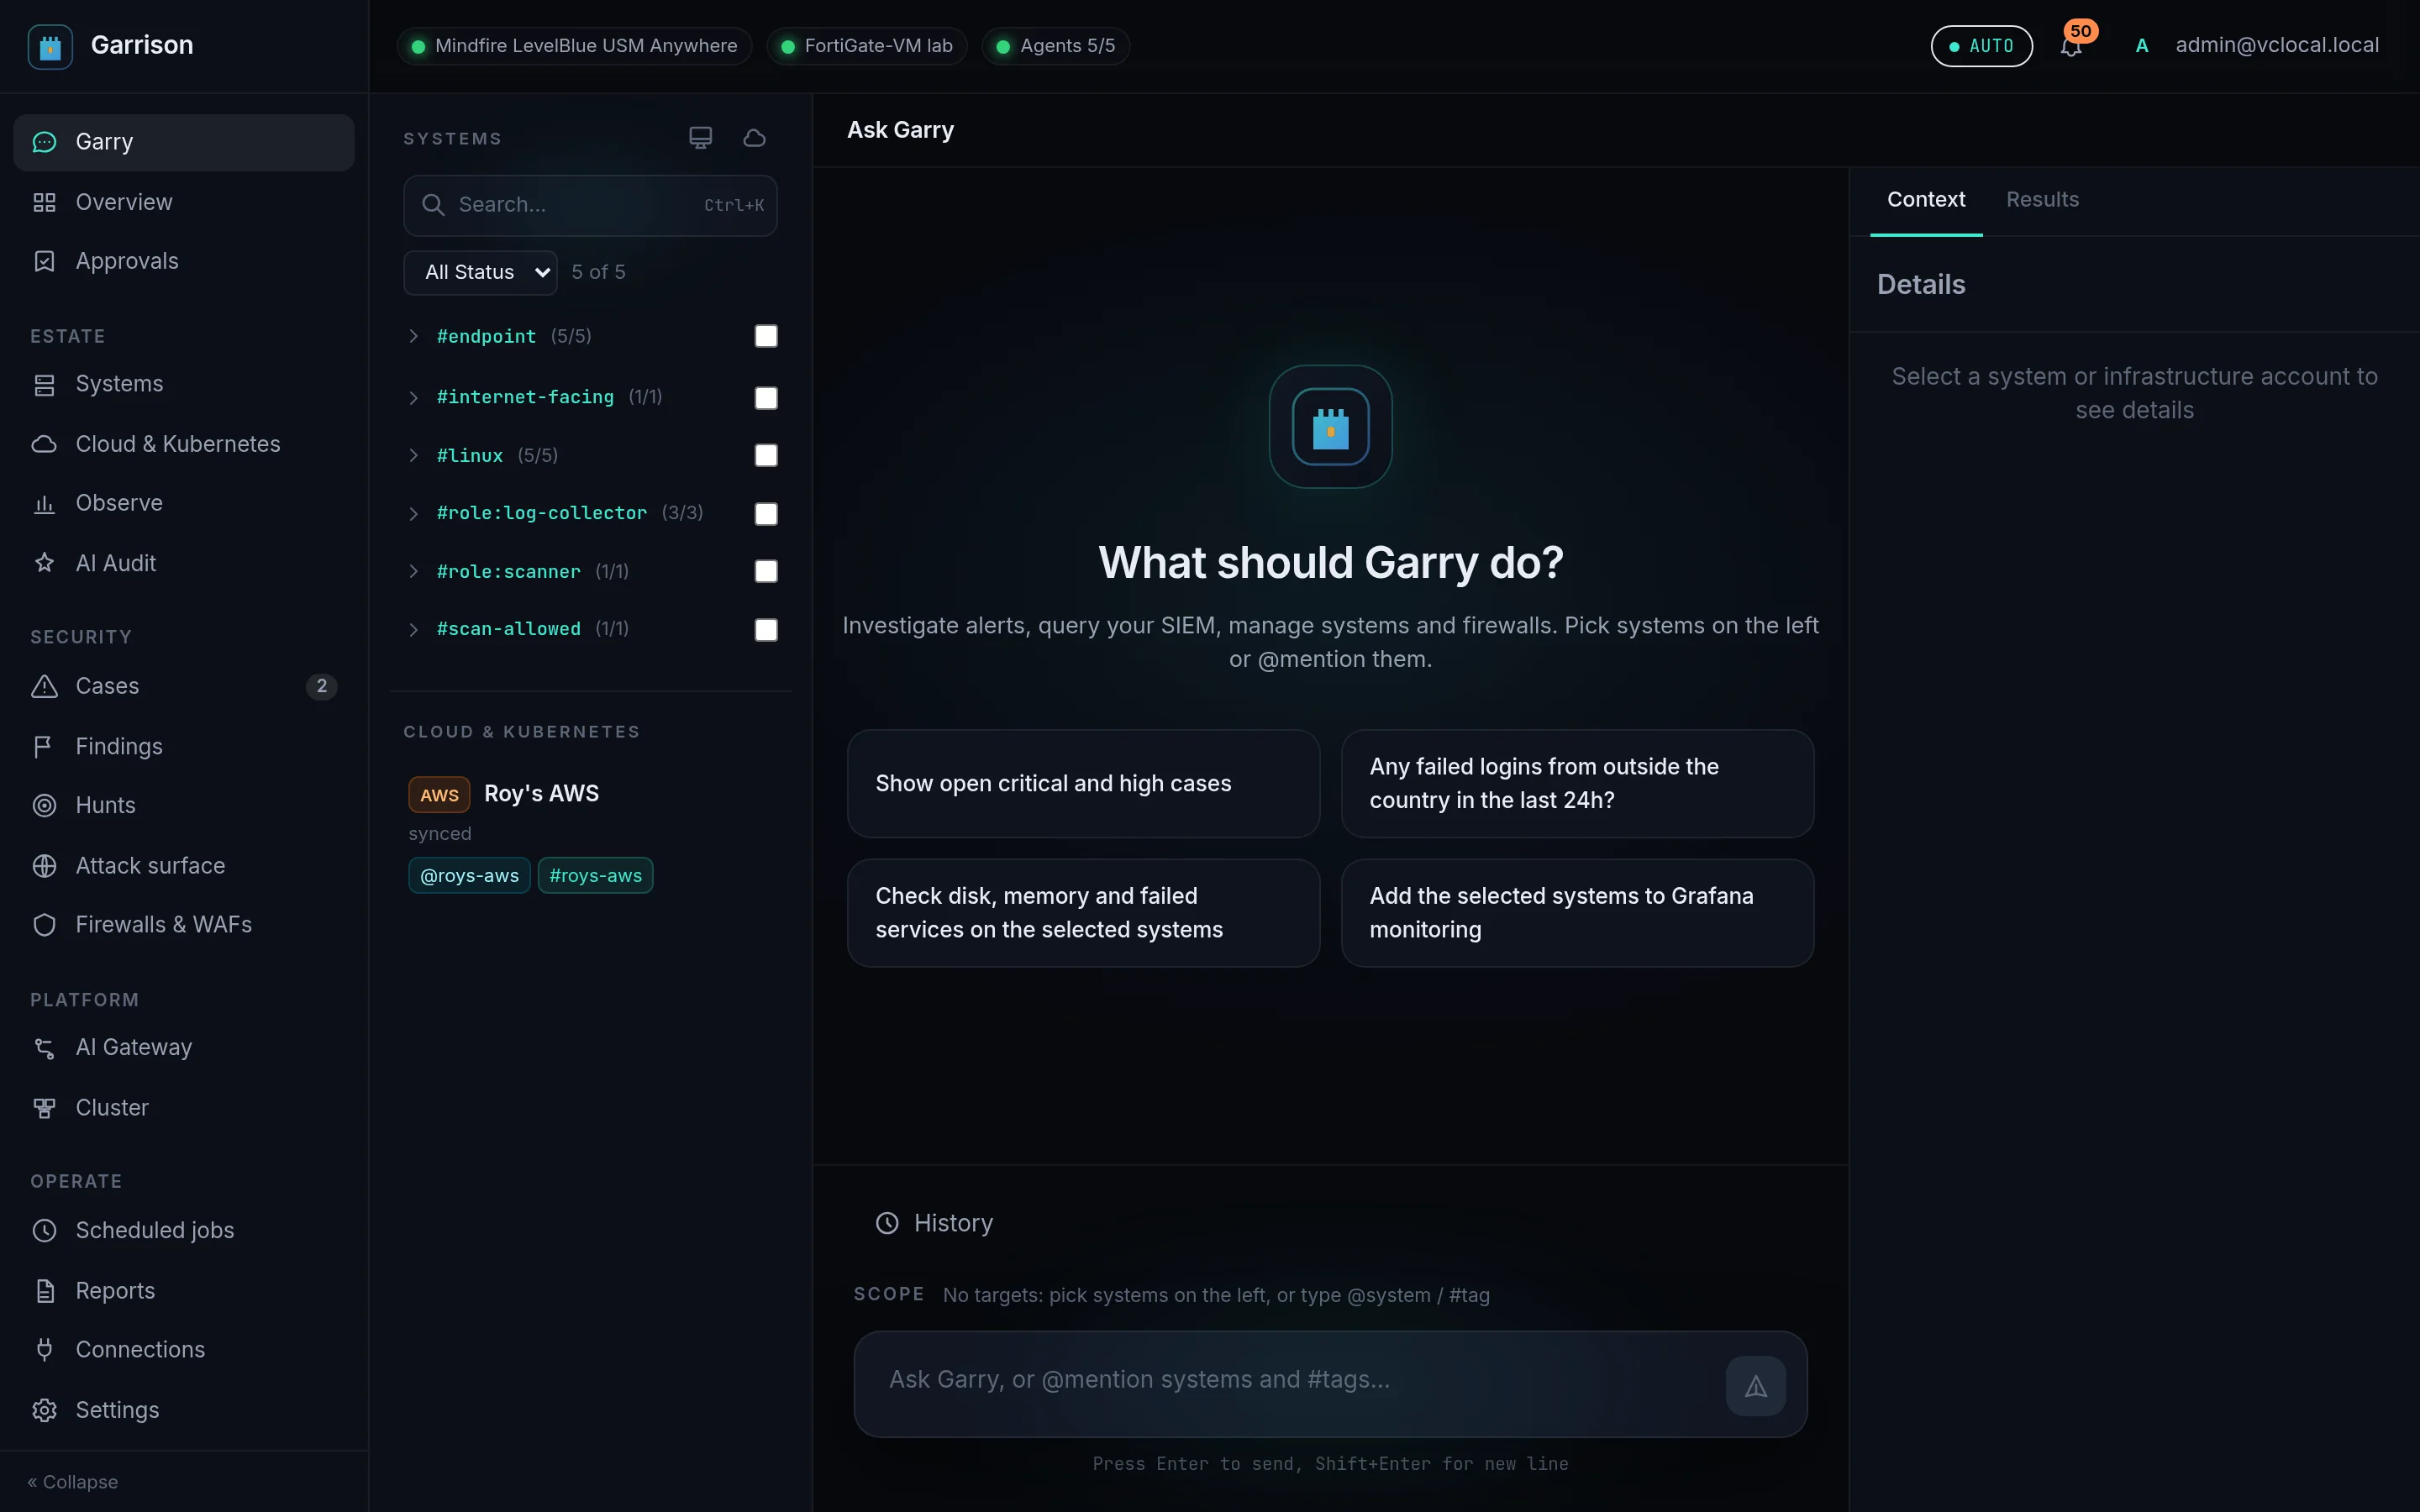
Ask Garry
Look after the estate in plain language: "check disk, memory and failed services on #prod", "why is nginx failing on web-01?". Read-only checks run at once; fixes are drafted for your approval.
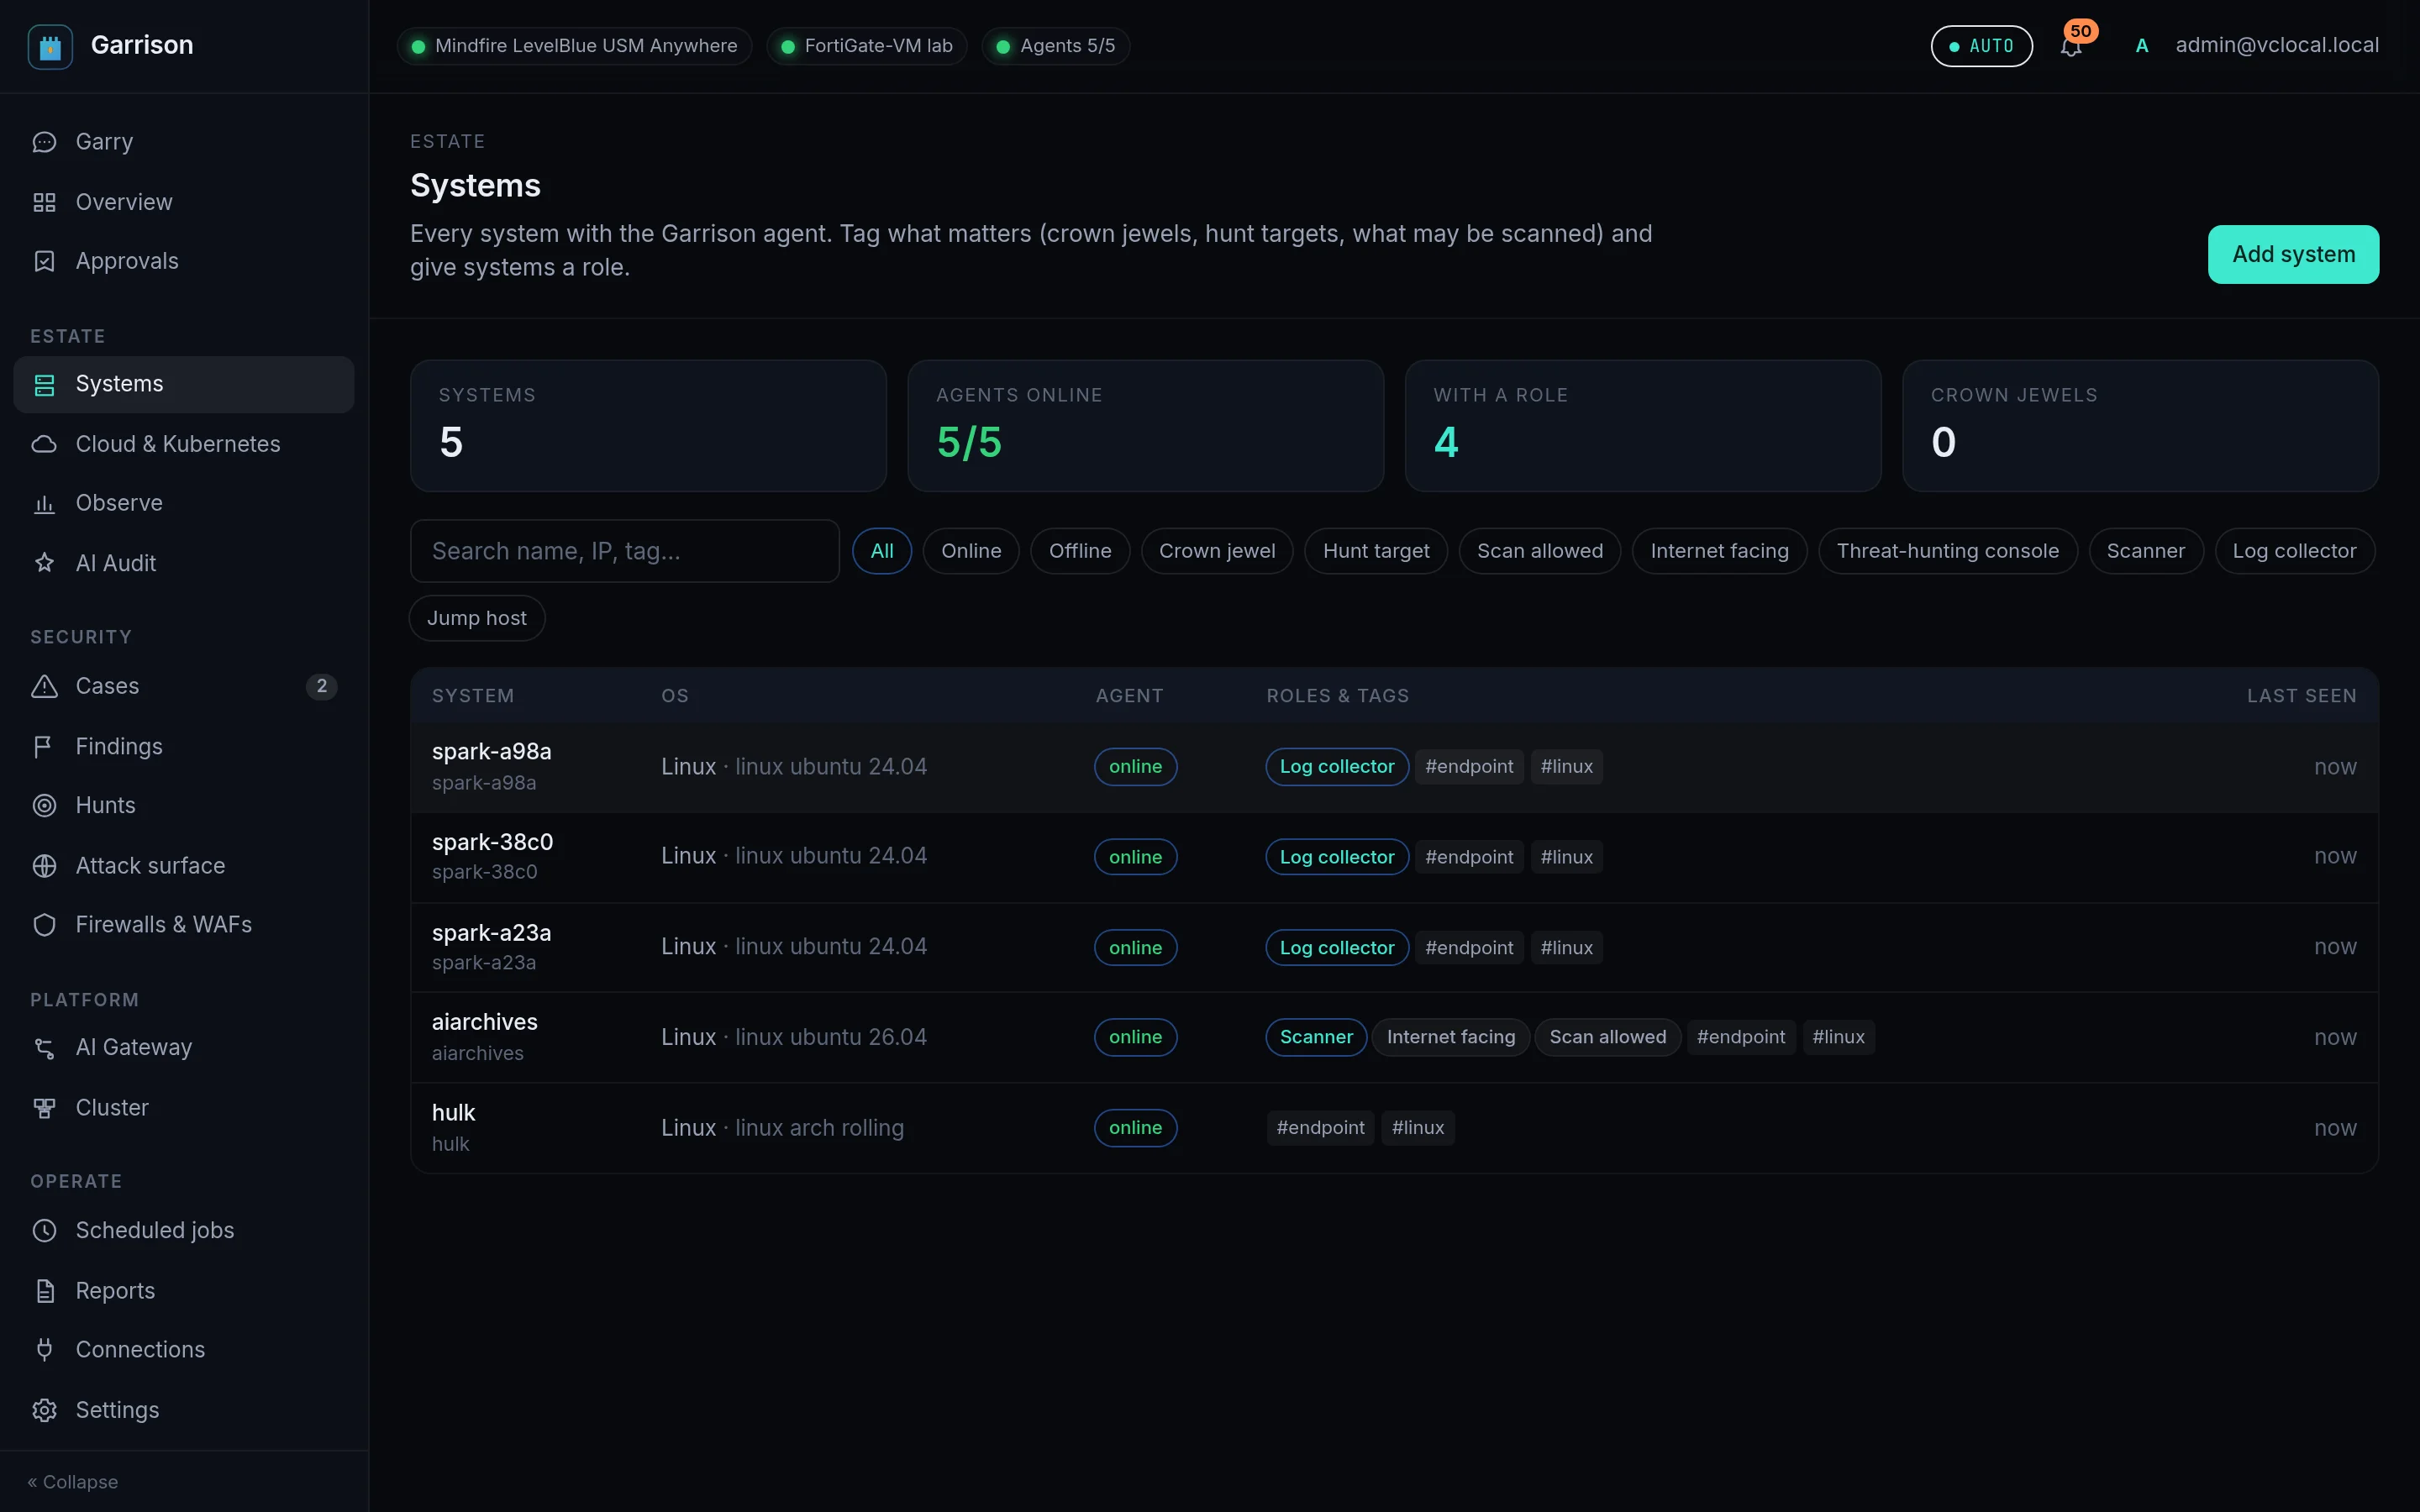
Every system in one place
Linux and Windows machines with a one-line agent: health, hardware, tags and roles. Make a system a log collector, a hardened jump host or a scanner with one approval.
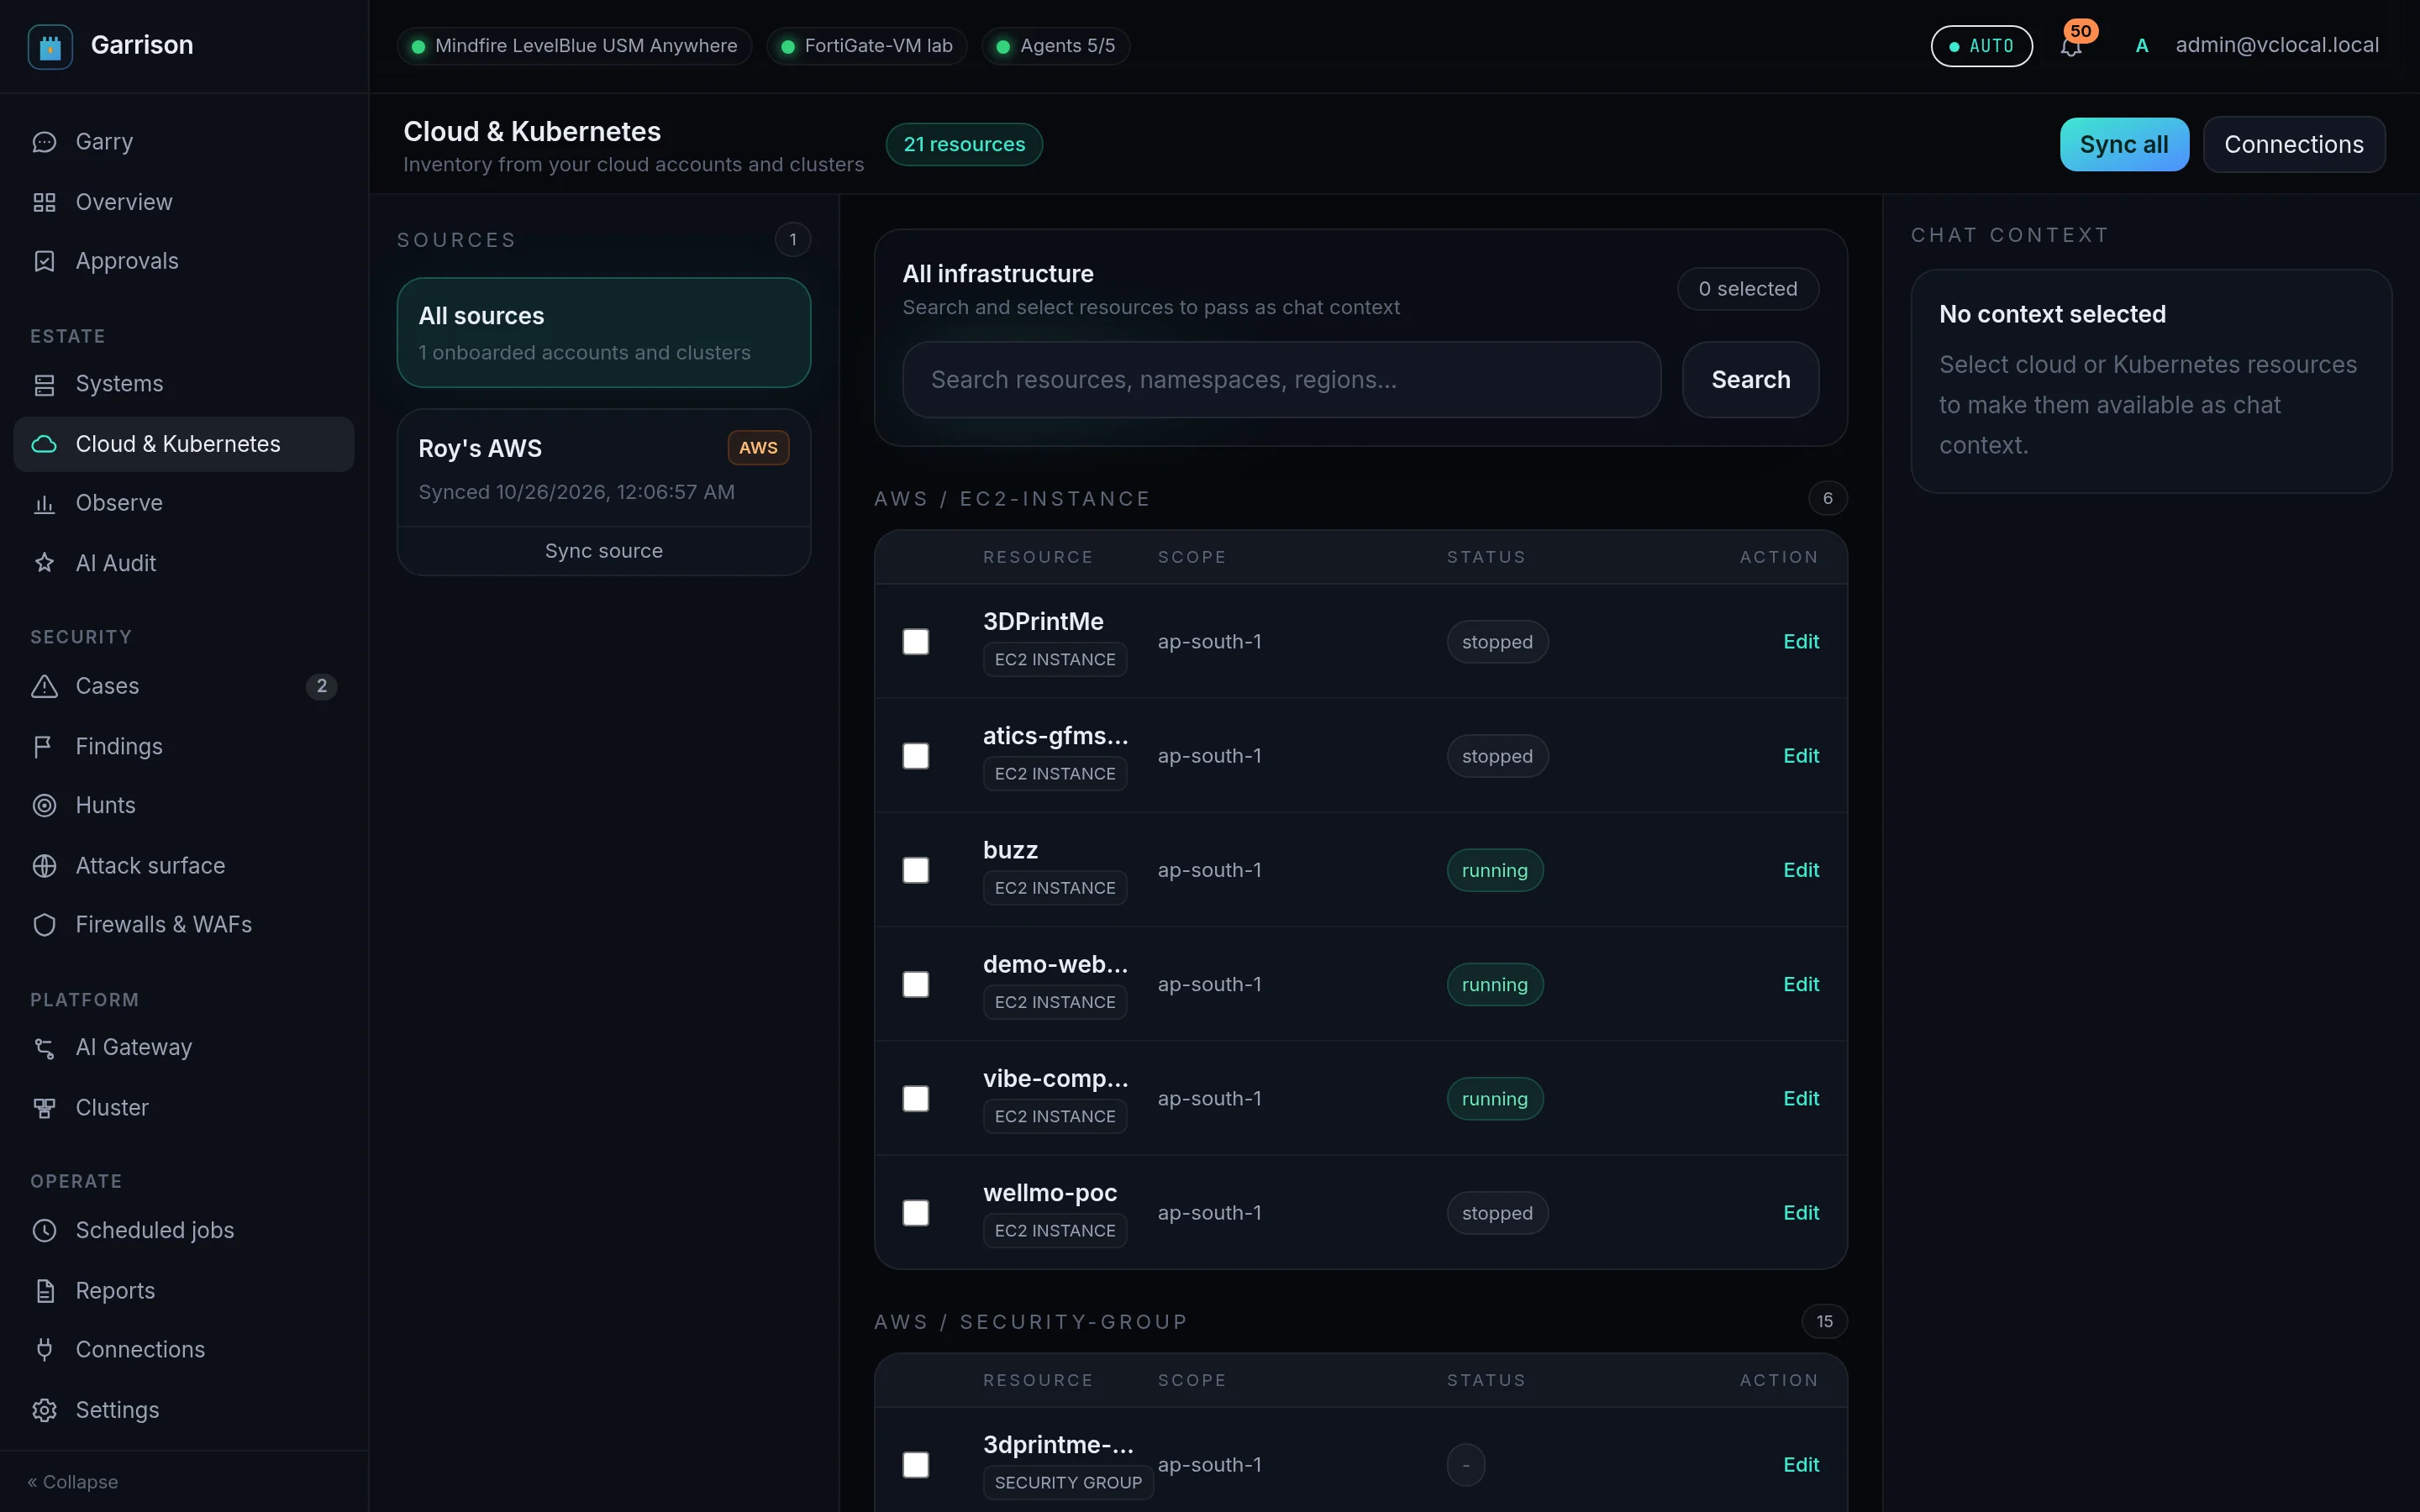
Cloud and Kubernetes
AWS, Azure, Kubernetes and Hetzner in one inventory. Ask what is running, what it costs and what is exposed; changes to the account are proposed and approved.
Monitoring and automation
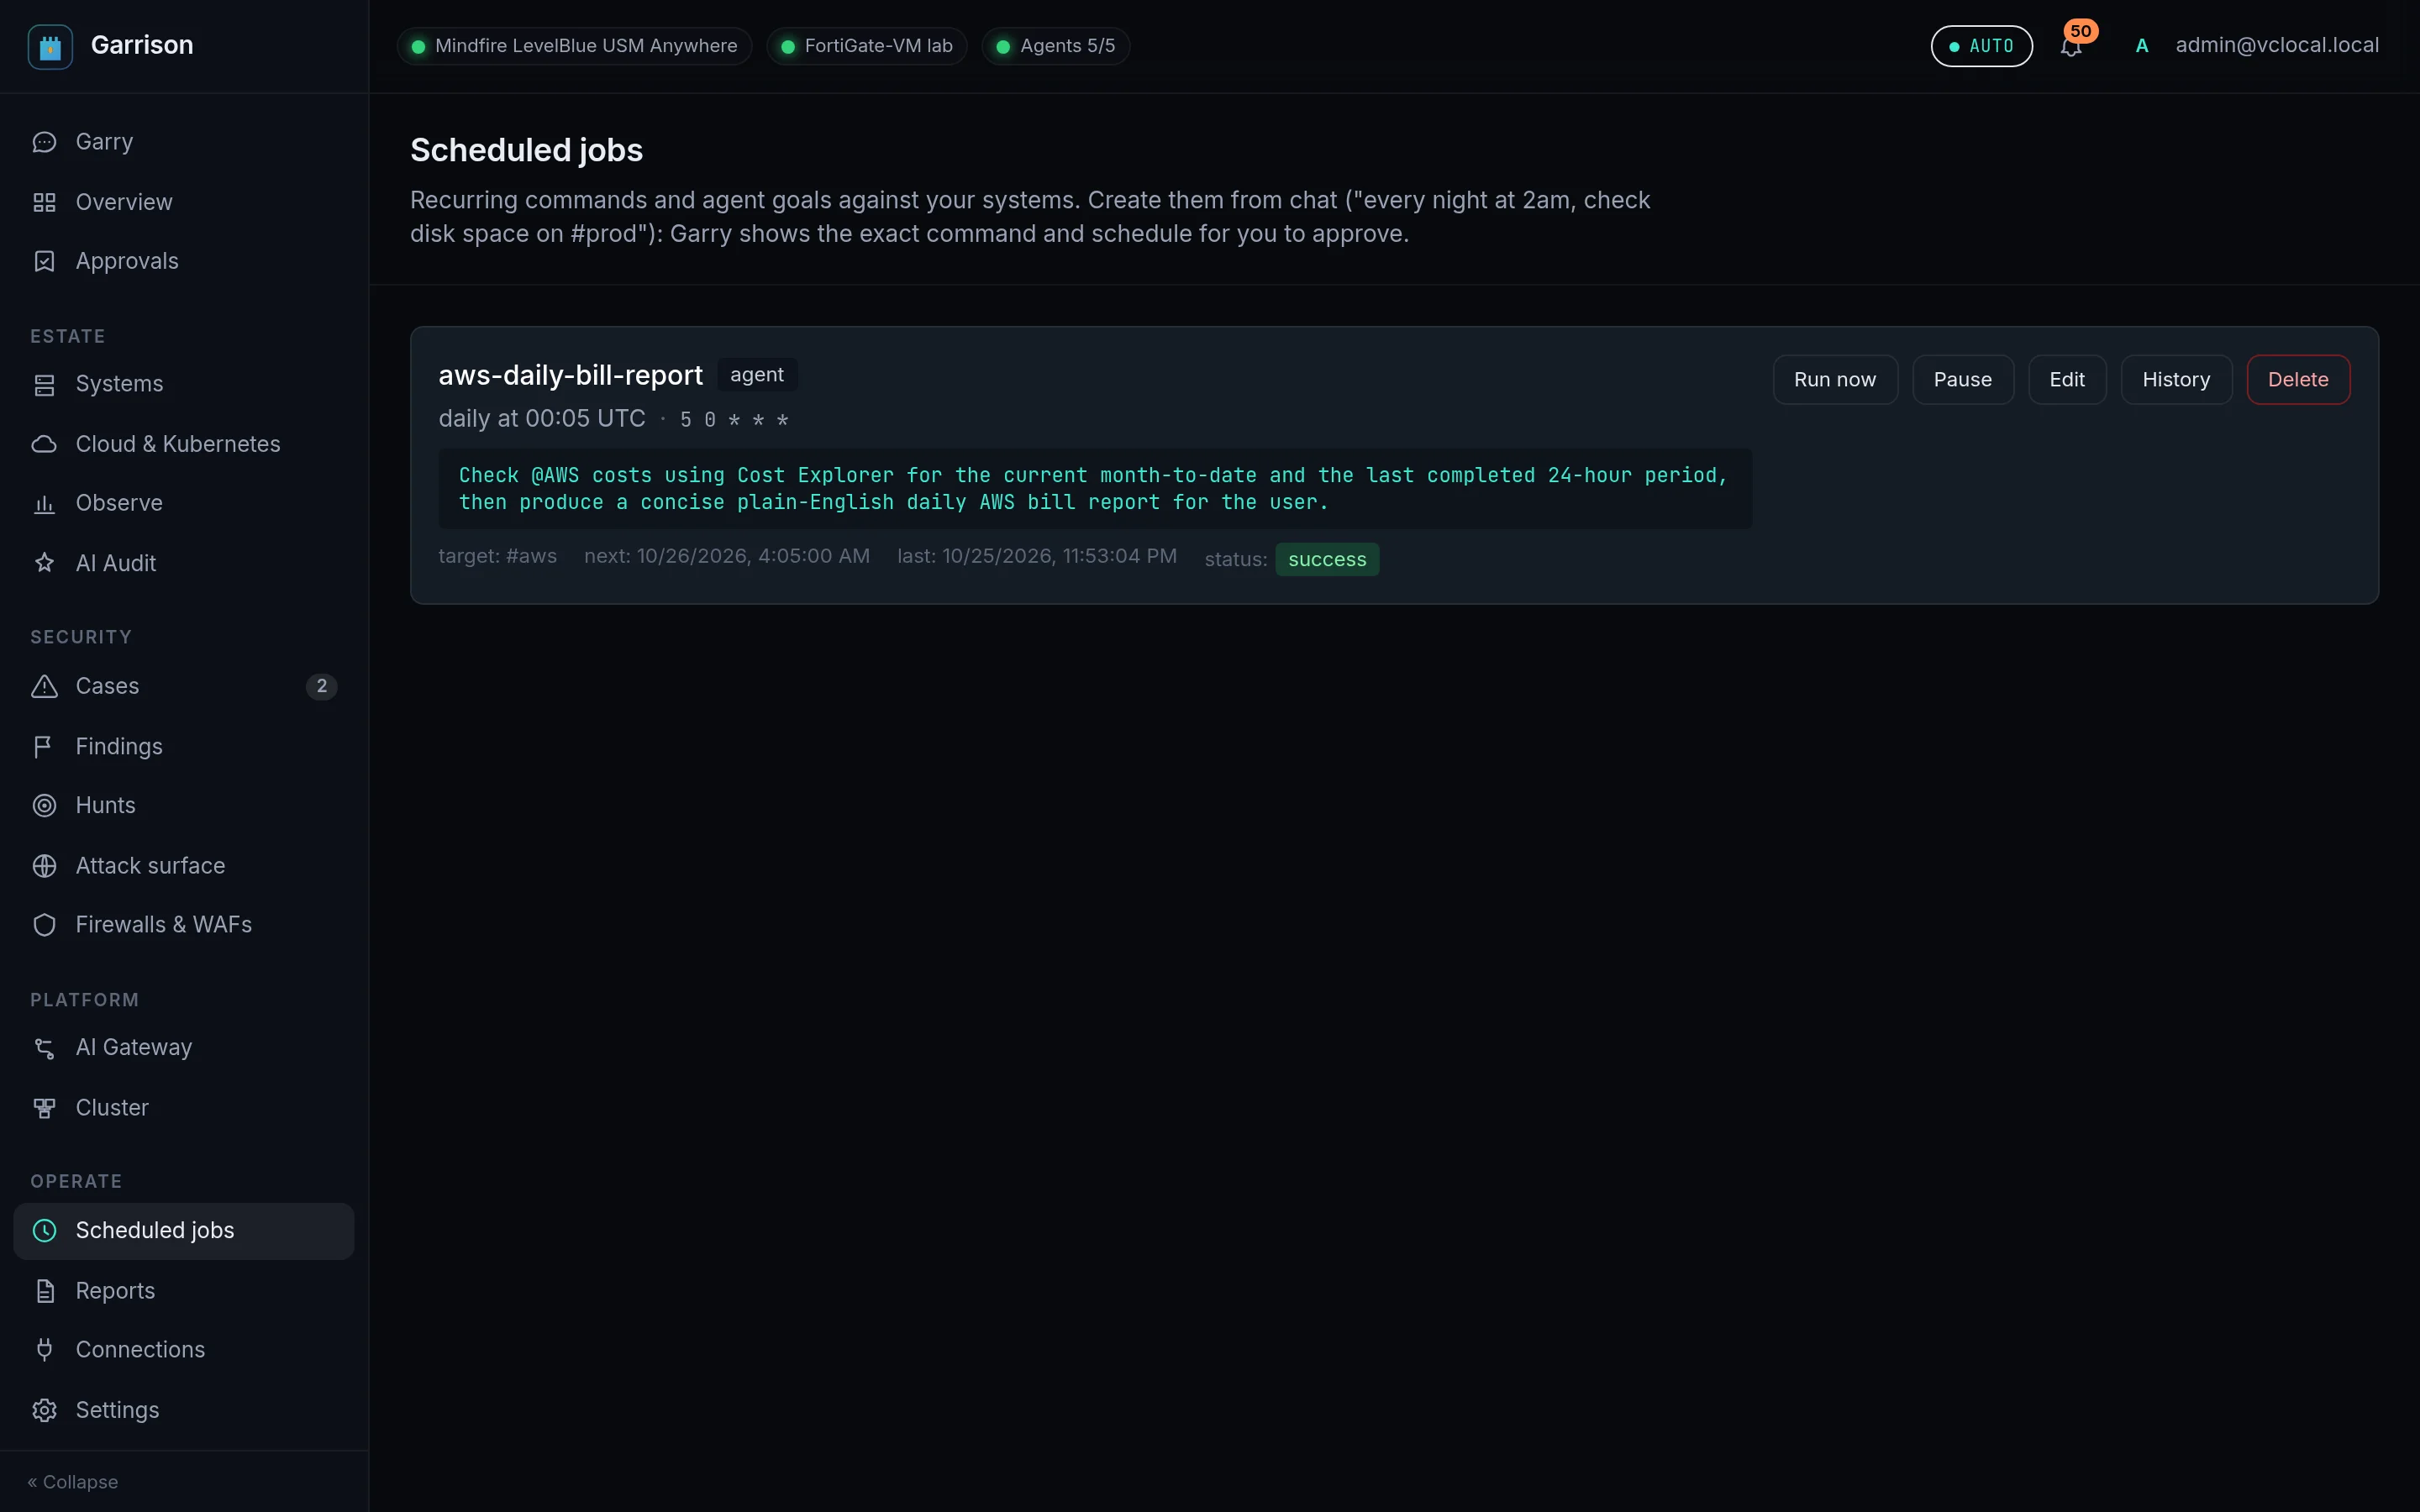
Logs, metrics and dashboards from every system, and recurring checks that report back. Each job shows its exact command and schedule.
Security, on the same console.
The agents, connectors and approvals that run your estate also defend it.
Alerts become cases
SIEM alerts clustered into cases, enriched with asset context and drafted for an analyst, who sets the verdict from the keyboard.
→Threat hunts
Hypotheses mapped to MITRE ATT&CK, scoped to the systems you choose, on a schedule or on demand.
→Attack surface
Certificates, ports and exposures on the targets you authorize, as findings with compliance references.
→Firewalls and WAFs
Configuration history and drift on FortiGate, Cloudflare and AWS WAF, with approved, verified, reversible blocks.
→The appliance decides what runs. Not the AI.
- Read-only by verificationA step runs on its own only when the appliance proves it cannot change anything.
- Approve exactly what you sawApproving runs the stored proposal, never other text a request carries.
- Agents connect outNo inbound ports on your systems; installs are pinned to your appliance's key.
- Everything auditedEvery command, terminal session, approval and AI prompt is recorded.
- Private by designModels run on the appliance; nothing leaves unless you connect an outside model.
See Garrison on your estate.
A proof of concept on your own servers, cloud accounts and SIEM, on an appliance in your network. Garrison runs on the open-source Open Agent Fabric.